Hejto.pl
Dodaj post

Wpisz coś do wyszukania (minimum 2 znaki)

#informatyka

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.17.md

MacOS Infection Vector: Using AppleScripts to bypass Gatekeeper - https://pberba.github.io/security/2025/11/11/macos-infection-vector-applescript-bypass-gatekeeper/

[Research] LLVM based VMProtect Devirtualization: Part 1 (EN) - https://hackyboiz.github.io/2025/09/11/banda/LLVM_based_VMP/en/

Making CloudFlare Workers Work for Red Teams - https://blog.zsec.uk/capd/

N-able N-central: From N-days to 0-days - https://horizon3.ai/attack-research/attack-blogs/n-able-n-central-from-n-days-to-0-days/

Corrupting the Hive Mind: Persistence Through Forgotten Windows Internals - https://www.praetorian.com/blog/corrupting-the-hive-mind-persistence-through-forgotten-windows-internals/

GURU

w Ciekawostki

29piorunów

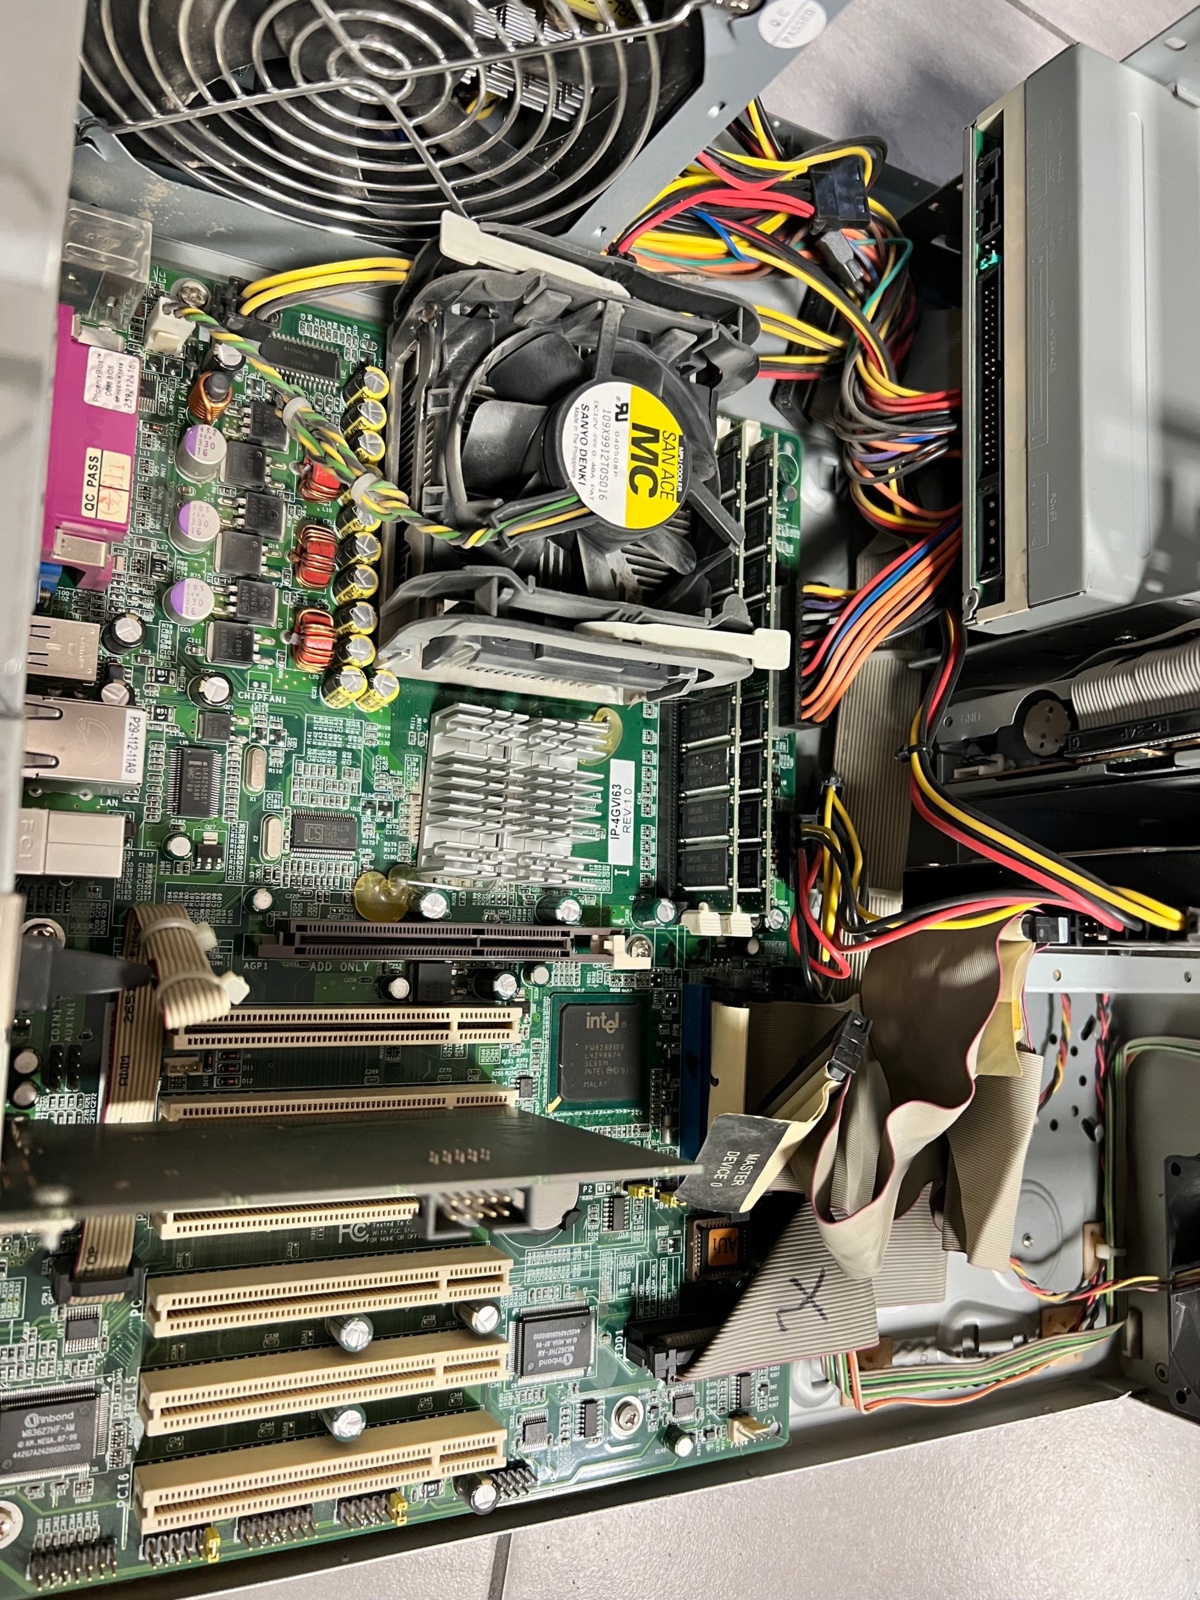
Hello there, my old friend (✿❦ ͜ʖ ❦)

„Nie działa klawiatura i mysz, nie uruchamia się”

> Wymienia baterie BIOS i ustawia w nim zasilanie USB

> Pora na CS’a

Pokaż więcej komentarzy (10)

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.15.md

An Introduction to Bypassing User Mode EDR Hooks - https://malwaretech.com/2023/12/an-introduction-to-bypassing-user-mode-edr-hooks.html

Reverse Engineering Binaries With AI - https://landaire.net/reverse-engineering-with-ai/

A Cracker Barrel vulnerability - https://eaton-works.com/2025/11/17/cracker-barrel-hack/

Achieving remote code execution in LangSmith Playground using unsafe template formatting - https://lab.ctbb.show/research/langsmith-unsafe-formatting-to-rce

Introducing Julius: Open Source LLM Service Fingerprinting - https://www.praetorian.com/blog/introducing-julius-open-source-llm-service-fingerprinting/

Mocarz

w Wiadomości Polska

4piorunów

Polska przygotowuje się na erę technologii kwantowych

:computer: :robot_face: Kwantowy skok Polski: Ministerstwo Cyfryzacji odsłania karty To już nie są wizje rodem z literatury science-fiction, ale twarda walka o suwerenność technologiczną. Ministerstwo Cyfryzacji ogłosiło zakończenie prac nad zaktualizowanymi Założeniami Polityki Rozwoju

Mocarz

w Dyskusje

12piorunów

Wow. Ciekawe czy też dał go na public domain tak jak kiedyś ten drugi algorytm kompresji video i złodziejski big tech przywłaszczył sobie patent?

Nowy standard zapisu zdjęć z polskim algorytmem zastępuje JPEG używany od 30 lat; nazwa to JPEG XL i może zmniejszyć rozmiar plików o kilkadziesiąt % przy wyższej jakości obrazu.

Sercem technologii jest algorytm ANS, który stworzył dr Jarosław Duda z Uniwersytetu Jagiellońskiego. Od początku 2026 format wspierają najpopularniejsze przeglądarki oraz Windows. Mniejsze pliki to szybsze ładowanie stron internetowych i oszczędność energii.

JPEG XL obsługuje nowoczesne funkcje jak HDR, przezroczystość czy animacje. Jest już wdrażany w medycynie (obrazowanie).

Tytan1piorunów

Bajzel prawny i patenty na kodeki oraz kodowanie to jeden z głównych hamulcowych we wprowadzaniu do użytku nowych formatów.
JPG na dzisiejsze standardy to gówniany format, a GIF to po prostu gówniany format :p. Ale są używane dlatego, że wspiera je wszystko oraz to że nie trzeba sie brabrać w tym prawnym gównie.

Z formatami video nie jest lepiej.
Nawet Nokia, która niegdyś była innowacyjna zdegradowała sie do roli trolla patentowego przez którego nie można
kupić ASUSa ani Acera w europe bo patent na H265 (link).

Paradoksalnie w przypadku formatów Google, które jest tym złym dla JPEGXL. Bo patent na ANS oraz walka z implementacją w Chrome. Tak wszystkie inne formaty, które wprowadzili (webp, avif, AV1, webm, VP9) są royalty-free do użytku bez ograniczeń.

Attention Required! | CloudflareVideocardz
Pokaż więcej komentarzy (3)

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.13.md

BodySnatcher (CVE-2025-12420): A Broken Authentication and Agentic Hijacking Vulnerability in ServiceNow - https://appomni.com/ao-labs/bodysnatcher-agentic-ai-security-vulnerability-in-servicenow/

Arbitrary App Installation on Intune Managed Android Enterprise BYOD - https://jgnr.ch/sites/android_enterprise.html

ARM64 Reversing And Exploitation Part 4 – Using mprotect() to bypass NX Protection - https://8ksec.io/arm64-reversing-and-exploitation-part-4-using-mprotect-to-bypass-nx-protection-8ksec-blogs/

No Leak, No Problem – Bypassing ASLR with a ROP Chain to Gain RCE - https://modzero.com/en/blog/no-leak-no-problem/

Developing An AI Vishing Model For £37.49 - https://http418infosec.com/developing-an-ai-vishing-model-for-37-49

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.11.md

Defeating Windows DEP Using ROP Chains Leveraging VirtualAlloc - https://screetsec.com/blog/defeating-windows-dep-using-rop-chains-leveraging-virtualalloc

When Windows takes a nap and leaves you evidence: Inside hiberfil.sys - https://www.magnetforensics.com/blog/when-windows-takes-a-nap-and-leaves-you-evidence-inside-hiberfil-sys/

CVE-2025-68668: Breaking Out of the Python Sandbox in n8n - https://www.smartkeyss.com/post/cve-2025-68668-breaking-out-of-the-python-sandbox-in-n8n

A 0-click exploit chain for the Pixel 9 Part 1: Decoding Dolby - https://projectzero.google/2026/01/pixel-0-click-part-1.html

Competing in Pwn2Own ICS 2022 Miami: Exploiting a zero click remote memory corruption in ICONICS Genesis64 - https://doar-e.github.io/blog/2023/05/05/competing-in-pwn2own-ics-2022-miami-exploiting-a-zero-click-remote-memory-corruption-in-iconics-genesis64/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.09.md

Next Generation Endpoint Security Check Your Privilege: The Curious Case of ETW's SecurityTrace Flag - https://www.originhq.com/blog/securitytrace-etw-ppl

RondoDox v2: Evolution of RondoDox Botnet with 650% More Exploits - https://beelzebub.ai/blog/rondo-dox-v2/

CVE-2025-43530: Exploiting a private API for VoiceOver - https://jhftss.github.io/CVE-2025-43530/

Privilege Escalation With Jupyter From the Command Line - https://www.adversis.io/blogs/privilege-escalation-with-jupyter-from-the-command-line

LANDFALL: New Commercial-Grade Android Spyware in Exploit Chain Targeting Samsung Devices - https://unit42.paloaltonetworks.com/landfall-is-new-commercial-grade-android-spyware/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.07.md

Self-XSS in Facebook payments flow leads to Instagram and Facebook account takeovers - https://ysamm.com/uncategorized/2025/01/15/self-xss-facebook-payments.html

TP-Link ER605 DDNS Pre-Auth RCE: Chaining CVE-2024-5242, CVE-2024-5243, CVE-2024-5244 - https://oobs.io/posts/er605-1day-exploit/

The Shady World of IP Leasing - https://acid.vegas/blog/the-shady-world-of-ip-leasing/

A Race Within A Race: Exploiting CVE-2025-38617 in Linux Packet Sockets - https://blog.calif.io/p/a-race-within-a-race-exploiting-cve

Avira: Deserialize, Delete and Escalate - The Proper Way to Use an AV - https://blog.quarkslab.com/avira-deserialize-delete-and-escalate-the-proper-way-to-use-an-av.html

Mocarz

w Technologia

8piorunów

Chat GPT 5.4 | możliwości, funkcje i zastosowania AI

:robot_face: Możliwości modelu GPT-5.4 i natywna obsługa komputera Firma OpenAI ogłosiła wprowadzenie nowej funkcjonalności o nazwie „Computer Use”. Wdrożenie to oznacza, że model GPT-5.4 zyskał możliwość operowania poza oknem przeglądarki internetowej. Po nadaniu odpowiednich

Zawodowiec

w Programowanie

8piorunów

Kolejność wiadomości w systemach rozproszonych - devszczepaniak.pl

Problem kolejności przetwarzania wiadomości to obok exactly-once delivery jedno z największych wyzwań systemów rozproszonych. Już sama detekcja problemu bywa skomplikowana, nie mówiąc o jego rozwiązaniu.\ \ W najnowszym artykule na blogu pokazuję, na jakie problemy związane z

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.05.md

CVE-2025-8556 - Cryptographic Issues in Cloudflare’s CIRCL FourQ Implementation - https://www.botanica.software/blog/cryptographic-issues-in-cloudflares-circl-fourq-implementation

Windows ARM64 Internals: Deconstructing Pointer Authentication - https://www.originhq.com/blog/windows-arm64-internals-deconstructing-pointer-authentication

Sniffing established BLE connections with HackRF One - https://blog.lexfo.fr/sniffing-ble-sdr.html

hackerbot-claw: An AI-Powered Bot Actively Exploiting GitHub Actions - Microsoft, DataDog, and CNCF Projects Hit So Far - https://www.stepsecurity.io/blog/hackerbot-claw-github-actions-exploitation

Vectored Exception Handling Squared - https://fluxsec.red/vectored-exception-handling-squared-rust

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.03.md

When NAS Vendors Forget How TLS Works - https://www.interruptlabs.co.uk/articles/when-nas-vendors-forget-how-tls-works

TP-Link Tapo C200: Hardcoded Keys - https://www.evilsocket.net/2025/12/18/TP-Link-Tapo-C200-Hardcoded-Keys-Buffer-Overflows-and-Privacy-in-the-Era-of-AI-Assisted-Reverse-Engineering/

Pentesting Next.js Server Actions - https://www.adversis.io/blogs/pentesting-next-js-server-actions

From DDS Packets to Robot Shells: - https://boschko.ca/unitree-go2-rce/

Pwning Claude Code in 8 Different Ways - https://flatt.tech/research/posts/pwning-claude-code-in-8-different-ways/

Fenomen

w Hydepark

1piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.03.01.md

Bypassing Apache FOP Postscript Escaping to reach GhostScript - https://offsec.almond.consulting/bypassing-apache-fop-escaping-to-reach-ghostscript.html

The "Ghost" in the Annotations - https://defensendepth.substack.com/p/the-ghost-in-the-annotations

Spring Boot Actuator - Using misconfigurations to your advantage: paths, bypasses, techniques - https://www.dsecured.com/en/articles/spring-boot-actuator-using-misconfig-to-your-advantage-paths-bypasses-techniques

Datr cookie theft and AI leads to Facebook account takeover via trusted device recovery - https://ysamm.com/uncategorized/2025/01/15/steal-dtsg-cookie.html

The Forgotten Bug: How a Node.js Core Design Flaw Enables HTTP Request Splitting - https://r3verii.github.io/cve/2026/02/27/nodejs-toctou.html

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.02.28.md

HonoJS JWT/JWKS Algorithm Confusion - https://devansh.bearblog.dev/honojs/

Desktop Window Manager Array Out Of Bounds LPE - https://ssd-disclosure.com/desktop-window-manager-array-out-of-bounds-lpe/

The security paradox of local LLMs - https://quesma.com/blog/local-llms-security-paradox/

TARmageddon (CVE-2025-62518) - https://edera.dev/stories/tarmageddon

Operation MacroMaze: new APT28 campaign using basic tooling and legit infrastructure - https://lab52.io/blog/operation-macromaze-new-apt28-campaign-using-basic-tooling-and-legit-infrastructure/

Mocarz

w Dyskusje

8piorunów

No to wjechało synology 225+ z 12gb ram i 18tb w raid1.

Tanie to nie było ale fotki z googla już się pobierają a z telefonu się synchronizują. I 5 tb filmów do domowego kekfliksa już siedzą :smiley:

A jeszcze tyyyle pomysłów mam na to

back to the pirate

Gruba ryba1piorunów

@EvilDick ja uzywam od 3 miechow ugreen i tez chwale sobie mozliwosc trzymania fotosow na chacie

Pokaż więcej komentarzy (8)

GURU

w Hydepark

15piorunów

Pokaż więcej komentarzy (13)

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.02.26.md

LockBit Returns — and It Already Has Victims - https://blog.checkpoint.com/research/lockbit-returns-and-it-already-has-victims/

ARM64 Reversing and Exploitation Part 3 - A Simple ROP Chain | 8kSec Blogs - https://8ksec.io/arm64-reversing-and-exploitation-part-3-a-simple-rop-chain/

pyLDAPGui - How It was Born - https://blog.zsec.uk/pyldapgui/

Leveraging Machine Learning to Enhance Acoustic Eavesdropping Attacks (Part 1 of 4) - https://cc-sw.com/leveraging-machine-learning-to-enhance-acoustic-eavesdropping-attacks-part-1-of-4/

Unlocking free WiFi on British Airways - https://saxrag.com/tech/reversing/2025/06/01/BAWiFi.html

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.02.24.md

Modding And Distributing Mobile Apps with Frida - https://pit.bearblog.dev/modding-and-distributing-mobile-apps-with-frida/

Achieving remote code execution in LangSmith Playground using unsafe template formatting - https://lab.ctbb.show/research/langsmith-unsafe-formatting-to-rce

Windows User Mode Exploit Development: Part 1 - https://memn0ps.github.io/windows-user-mode-exploit-development-part-1/

Singularity: Deep Dive into a Modern Stealth Linux Kernel Rootkit - https://blog.kyntra.io/Singularity-A-final-boss-linux-kernel-rootkit

Drone Hacking Part 1: Dumping Firmware and Bruteforcing ECC - https://neodyme.io/en/blog/drone_hacking_part_1/#intro

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.02.22.md

Hacking Furbo - A Hardware Research Project – Part 2: Mobile and P2P Exploits - https://www.softwaresecured.com/post/hacking-furbo-a-hardware-research-project-part-2-mobile-and-p2p-exploits

PureVPN IPv6 leak - https://anagogistis.com/posts/purevpn-ipv6-leak/

Why nested deserialization is STILL harmful – Magento RCE (CVE-2025-54236) - https://slcyber.io/research-center/why-nested-deserialization-is-still-harmful-magento-rce-cve-2025-54236/

Casting a Net(ty) for Bugs, and Catching a Big One (CVE-2025-59419) - https://depthfirst.com/post/casting-a-net-ty-for-bugs-and-catching-a-big-one-cve-2025-59419

Critical Account Takeover via Unauthenticated API Key Creation in better-auth (CVE-2025-61928) - https://zeropath.com/blog/breaking-authentication-unauthenticated-api-key-creation-in-better-auth-cve-2025-61928