Hejto.pl
Dodaj post

Wpisz coś do wyszukania (minimum 2 znaki)

konik_polanowyFenomen

Dołączył/a:

  • 1471 wpisów
  • 157 komentarzy
  • 36 obserwujących

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.27.md

TAPOcalypse Now: Exploiting TP-Link Smart Devices From Anywhere - https://labs.taszk.io/articles/post/tapocalypse/

eMudhra Intermediate CA Compromise - https://emudhra.we-have-a-problem.com/

When Defenses Become Attack Surface: CVE-2026-20971, a Samsung Kernel UAF - https://lucidbitlabs.com/blog/when-defenses-become-attack-surface/

Don't Let Abliteration Abliterate Your Bug Hunting: Discovering Verdict Bias in Uncensored Models - https://clearbluejar.github.io/posts/does-abliteration-skew-your-bug-hunting/

One Parser, Two Bugs, Many Routers: Exploiting Broadcom WiFi Across eCos and Linux h- ttps://quentinkaiser.be/security/2026/10/16/one-parser-two-bugs/
Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.25.md

Dumping Encrypted Viltrox Lens Firmware - two Times - https://blog.29b.net/dispatches/viltrox_re/

PhantomBuffer: Effective EDR Evasion Through Stealth Injection - https://www.zerosalarium.com/2026/10/PhantomBuffer-Effective-EDR-Evasion-Stealth-Injection.html

Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers - https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

Hiding a DLL from the PEB Loader List (And Why Process Explorer Still Sees It) - https://trainsec.net/library/windows-internals/hiding-a-dll-from-the-peb-loader-list-and-why-process-explorer-still-sees-it/

LiteLLM compromised again: infostealer and RAT found in version 1.107.0 - https://www.aikido.dev/blog/litellm-compromised-infostealer-rat

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.23.md

Inside the Intel 8087 chip: floating-point addition and subtraction - https://www.righto.com/2026/10/8087-addition-subtraction-microcode.html

CloudKeyVaultEvents: Azure Key Vault Logs, Schema and KQL Hunting - https://kqlquery.com/posts/cloudkeyvaultevents/

Building a Malware Development Lab, Part 1: Elastic EDR with a Self-Hosted Elastic Stack - https://blog.bsdrip.tech/maldev-lab/01-elastic-edr-lab-setup/

Casse-Spip - From an Unauthenticated SQL Injection to Remote Command Execution - https://blog.lexfo.fr/casse-spip-sqli-to-rce.html

Microsoft Paint and Photos Embed Server-Issued GUIDs as Invisible Watermarks in Locally-Generated Images - https://xusheng.dev/posts/reversing/mspaint_invisible_watermark/main/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.21.md

ApeX v0.4: Metis - https://phantomsec.tools/blog/apex-c2-v04-release

No Time to Pwn: CVE-2026-72018 - https://xbow.com/blog/no-time-to-pwn-cve-2026-72018

All logic, no bite - https://blog.coredump.cx/p/all-logic-no-bite

PwnEscape (CVE-2026-99999): Patched kernels available in testing - https://almalinux.org/blog/2026-10-16-pwnescape-cve-2026-99999/

CVE-2026-23866: Finding a Whatsapp NDay - https://numb3rs.re/posts/cve-2026-23866-finding-a-whatsapp-nday/

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.19.md

Bypassing AMSI & ETW: Building a Custom PowerShell Runspace in C# - https://by7e.dev/blog/runspace

Detection Versioning: The evolution of logic and intent - https://nebulock.io/blog/detection-versioning-the-evolution-of-logic-and-intent

After You’re In: Field Notes on CRTO Prep and OPSEC - https://gikaku.net/2026/10/17/crto-opsec/

DLL Sideloading for Initial Access and Bypassing Elastic EDR - https://akchhat.gitbook.io/dev/initial-access/dll-sideloading-for-initial-access-and-bypassing-elastic-edr

How to use Codex for Bug Bounty research: explore broadly, validate rigorously - https://www.yeswehack.com/learn-bug-bounty/llm-series-codex

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.17.md

Google's PageBreak Project – Real-World Findings - https://bughunters.google.com/blog/pagebreak-real-world-findings

Following the Instructions: Live ARM Tracing with the ETM, ITM, and TPIU - https://voidstarsec.com/blog/arm-tracing-etm-itm

How I Could've Accessed 17 Trillion Microsoft Records - https://blog.faav.net/how-i-couldve-accessed-17-trillion-microsoft-records

CVE-2026-87902: WordPress Core unauthenticated path traversal in get page template page-template resolution leading to conditional RCE - https://www.pruva.dev/reproductions/REPRO-2026-00356

Running Tesla Model 3's Computer on My Desk Using Parts From Crashed Cars - https://bugs.xdavidhu.me/tesla/2026/03/23/running-tesla-model-3s-computer-on-my-desk-using-parts-from-crashed-cars/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.15.md

State of Identity: Active Directory - https://www.inde.nz/blog/state-of-identity-active-directory

NTDLL-Reconstruction - https://leosmith.wtf/blog/ntdll_reconstruction.html

The RP2350 security model - https://donjon.ledger.com/blog/rp2350-secure-debug-laser-fault-injection/

Oh Look, The Foot Gun Went Off Again (Citrix NetScaler PreAuth Command Injection CVE-2026-88771) - https://labs.watchtowr.com/oh-look-the-foot-gun-went-off-again-citrix-netscaler-preauth-command-injection-cve-2026-88771/

I handed the epoll UAF to an agent - https://guysrd.github.io/epoll-uaf-agent

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.13.md

Introducing Aikido Altar: the model that makes sovereign security intelligence possible - https://www.aikido.dev/blog/aikido-altar-open-weight-ai-sovereign-security

Learning LLVM (Part-1) - Writing a simple LLVM pass - https://sh4dy.com/2024/06/29/learning_llvm_01/

Harnessing Harnesses - Climbing the LLM Hills - https://blog.zsec.uk/harnessing-harnesses/

A story of wifi secrets, UART lockdowns and a damaged flash memory chip - https://adepts.of0x.cc/eufy-homestation2-firmware/

Disposable Tooling - Building LLM-Generated Mythic Agents from Prompt to Deployment - https://blog.xpnsec.com/disposable-tooling/

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.11.md

MECCHA CHAMELEON can't hide from the RCE - https://www.aikido.dev/blog/meccha-chameleon-rce

Abusing Constrained Delegation without Protocol Transition against SPN-less accounts - https://hunio.org/security/abusing-constrained-delegation-without-protocol-transition-against-spn-less-accounts/

Serving a (g)zip bomb with Caddy - https://dustri.org/b/serving-a-gzip-bomb-with-caddy.html

Active Directory Attack Architecture Map v2.0 - https://kypvas.github.io/ad_attack_architecture/

CVE-2026-81578: PaperCut NG/MF CVE-2026-81578 + CVE-2026-82078 unauthenticated RCE chain - https://www.pruva.dev/reproductions/REPRO-2026-00340

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.09.md

We burned 11.7bn tokens to find the best cyber AI model - https://www.aikido.dev/blog/ai-model-benchmarks-aug-21-2026

Nuclei vulnerabilities: Information Disclosure, Denial of Service - https://labs.stoik.io/nuclei-vulnerabilities-information-disclosure-denial-of-service-2/

Vulnerability Research on Bitdefender's Antivirus Engine - https://stackbits.eu/blog/vulnerability_research_bitdefender_part_1.html

From Physical Memory Read/Write to SYSTEM - https://vojtechhron.dev/en/article/ktapi-lpe

You're Building Your MCP Wrong - https://mpgn.fr/youre-building-your-mcp-wrong/

Fenomen

w Hydepark

2piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.07.md

Bypassing DEP: VirtualProtect - https://iss4cf0ng.github.io/2026/09/30/2026-9-30-DEP/

Learning LLVM (Part-1) - Writing a simple LLVM pass - https://sh4dy.com/2024/06/29/learning_llvm_01/

Microsoft Paint and Photos Embed Server-Issued GUIDs as Invisible Watermarks in Locally-Generated Images - https://xusheng.dev/posts/reversing/mspaint_invisible_watermark/main/

Module Stomping - The Standard Injection For Modern C2 Agents - https://combat.theater/blog/module-stomping/

Lunex Uses BYOVD to Disable Security Monitoring and Deploy Persistent Stealer - https://blog.polyswarm.io/lunex-uses-byovd-to-disable-security-monitoring-and-deploy-persistent-stealer

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.05.md

Backdoors in the Dungeon – TURN & MQTT Abused by DragonForce - https://lab52.io/blog/backdoors-in-the-dungeon-turn-mqtt-abused-by-dragonforce/

I accidentally logged hundreds of thousands of phone calls to military bases - https://lina.sh/blog/hijacking-e164-arpa

Inside the Sandbox: How pwn Escaped Google kvmCTF (Before the Watershed) - https://pwn.ai/blog/kvmescape

Frappe 16.18.3 / ERPNext 16.19.1 SSTI to OS RCE - https://thinkloveshare.com/offenskill/frappe-ssti-to-rce/

Hunting Abuse: Detecting Privilege Escalation Through the ADCS Database - https://www.guidepointsecurity.com/blog/detecting-privilege-escalaction-through-adcs/

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.03.md

Paint It Blue: Reversing Win32k's Callbacks - https://idov31.github.io/posts/paint-it-blue-reverse-win32k

Static Devirtualization of Tencent VM - https://aftermathlabs.net/blog/31/07/2026/

Dirty Cert: Cisco Smart Software Manager's Silently Patched RCE - https://starlabs.sg/blog/2026/09-dirty-cert-cisco-smart-software-managers-silently-patched-rce/

Two DGX Sparks, 33 Local Models, One Question: Can Local AI Actually Red Team? - https://betheadversary.com/posts/dgx_spark_red_team_bench/

Is sandboxing sufficient to contain rogue agents? - https://blog.cryptographyengineering.com/2026/09/30/is-sandboxing-sufficient-to-contain-rogue-agents/

Pokaż więcej komentarzy (4)

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.10.01.md

Exploiting Azure IMDS - https://cyberdom.blog/exploiting-azure-imds/

Windows Internals: Secure Calls - The Bridge Between The NT Kernel and Secure Kernel - https://connormcgarr.github.io/secure-calls-and-skbridge/

GDID: The Windows Global Device Identifier - https://zerotracelab.com/blog/gdid-windows-tracking

CVE-2026-20182: Critical authentication bypass in Cisco Catalyst SD-WAN Controller (FIXED) - https://www.rapid7.com/blog/post/ve-cve-2026-20182-critical-authentication-bypass-cisco-catalyst-sd-wan-controller-fixed/

WINDOWS PRIVILEGE ESCALATION USING NCSI ACTIVE PROBES - https://labs.itresit.es/2026/09/28/windows-privilege-escalation-using-ncsi-active-probes/

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.29.md

Discovering and exploiting a remote code execution vulnerability in OpenCode (GHSA-632h-h47v-g4x4) - https://securitylabs.datadoghq.com/articles/opencode-upgrade-remote-code-execution/

How I Could've Accessed 17 Trillion Microsoft Records - https://blog.faav.net/how-i-couldve-accessed-17-trillion-microsoft-records

A prompt that finds deep logic bugs, and the pipeline we built around it - https://workos.com/blog/vulnerability-analysis-pipeline

Even more privileged ADCS ESC_CES - https://adhdmurky.github.io/posts/post4/

I spent 3 years of my life building this tool- DIYFPV DRONE BUILDER - https://www.youtube.com/watch?v=uzM72CcgL0c

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.27.md

One Tap Too Far: Using Shortcuts to Bypass Chrome for iOS Call Prompts - https://blog.doyensec.com/2026/09/24/chrome-ios-policy-bypass.html

Containers Are No Longer a Security Boundary - https://depthfirst.com/research/containers-are-no-longer-safe

ceasta a disassembler, decompiler and debugger in one — for windows and linux - https://github.com/ngwg/ceasta

How One Twitch Chat Message Became Code Execution on a Streamer’s PC - https://blog.scrt.ch/2026/09/22/how-one-twitch-chat-message-became-code-execution-on-a-streamers-pc/

Llama.cpp, an Ice Cold CORS Light, and Command Execution - Put it on my Tab! - https://g3tsyst3m.com/cors/Llama.cpp,-an-Ice-Cold-CORS-Light,-and-Command-Execution-Put-it-on-my-Tab!/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.25.md

Testing race conditions with memory access tracing and stack-based delay injection - https://projectzero.google/2026/09/maccconc-race-condition.html

Photon-Emission-Guided Laser Fault Injection Enables RP2350 Secure Debug - https://donjon.ledger.com/blog/rp2350-secure-debug-laser-fault-injection/

When Defenses Become Attack Surface: CVE-2026-20971, a Samsung Kernel UAF - https://lucidbitlabs.com/blog/when-defenses-become-attack-surface/

CVE-2026-7162 Root Cause Analysis - https://blog.uhg.sg/cve/cve-2026-7162

LogonTracer v2 is a tool to investigate malicious logon by visualizing and analyzing Windows Active Directory event - https://github.com/JPCERTCC/LogonTracer

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.23.md

Evading Machine Learning Based Detections - https://msecops.de/blog/posts/ml-evasion/

Stop Using OpenCode - https://wren.wtf/shower-thoughts/stop-using-opencode/

AI studio Auth bypass - https://ndevtk.github.io/writeups/2026/07/28/ais-bypass/

Fileless ELF Execution via O_TMPFILE - https://matheuzsecurity.github.io/hacking/fileless-loader-bypassing-elastic-memfd/

Introducing Pretender - Your New Sidekick for Relaying Attacks - https://blog.redteam-pentesting.de/2022/introducing-pretender/

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.21.md

A Brilliantly Simple Bug In V8 - https://qedaudit.io/blog/brilliantly-simple/

The QNAP Pattern - https://runiclabs.io/research/qnap-architecture/

How to Run a Windows Service Inside Svchost.exe - https://trainsec.net/library/malware-analysis/how-to-run-a-windows-service-inside-svchostexe-service-dll-walkthrough/

SQL Injection - Bypassing Baffin Bay WAF to Exploit PostgreSQL ORDER BY Injection - https://p3n7a90n.github.io/blogs/sql-injection-waf-bypass-postgresql-order-by/

Writing Beacon Object Files In Mythic Using Dark Agent For MacOS - https://umsundu.co.uk/posts/Writing-Beacon-Object-Files-In-Mythic-Using-Dark-Agent-For-Mac/

Fenomen

w hejtoczyta

12piorunów

1257 + 1 = 1258

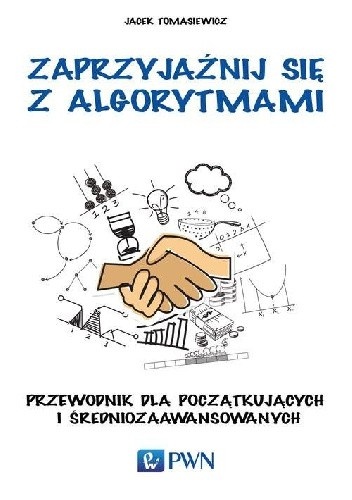
Tytuł: Zaprzyjaźnij się z algorytmami. Przewodnik dla początkujących i średniozaawansowanych

Autor: Jacek Tomasiewicz

Kategoria: informatyka, matematyka

Format: ebook

Ocena: 7/10

Książka bardziej do przerobienia niż do czytania. Zbiór zadań z poprzednich lat olimpiad matematycznych dla licealistów z dość dużymi zadatkami na studia matematyczne lub techniczne.

Wygenerowano za pomocą https://bookmeter.xyz